
A new type of cybercrime is seeing mind-boggling sums stolen in the world of digital finance and crypto currencies, according to ground-breaking research involving an academic at the University of Winchester.
A new article in the Journal of Financial Crime, co-authored by Professor Tim Hall of the of Winchester’s Department of Policing, Criminology and Forensics, and Remo Stieger, a former partner at SyntiFi Risk Intelligence, highlights the dangers of flash loan attacks on the DeFi (Decentralized Finance) ecosystem.
The pair identified 254 successful attacks on the DeFi ecosystem, resulting in losses $6.568 billion, between February 2020 and July 2024.
Of these attacks, 72 were flash loan attacks*, which resulted in losses $1.211 billion.
A flash loan lets someone borrow a very large amount of cryptocurrency without providing collateral, provided the loan is borrowed and repaid within the same blockchain transaction. Blockchain is shared digital ledger that allows banks, institutions, and individuals to record and verify financial transactions directly without relying on a middleman.
An attacker can use the borrowed money to manipulate prices, exploit faulty smart contracts, or take advantage of differences between exchanges. They then repay the loan and keep any profit. As everything happens almost instantly in one transaction, the attacker does not need to risk their own money.
Flash loans are legal - these attacks exploit weaknesses in DeFi systems.
Prof Hall said: “This research came about because of a shared concern about new criminal opportunities created by the advance of cryptocurrencies and blockchain technologies. We now are seeing crimes that we have never seen before and ones that are capable of stealing mind-boggling sums of money, often in the tens of millions of dollars.
“We saw the research as the perfect opportunity to combine the insights of SyntiFi's on-chain risk intelligence engine, which is capable of scanning billions of cryptocurrency transactions, with more context criminological analysis. As far as we are aware this is a unique partnership.
"We are keen that this isn't seen just as a piece of academic research. The analysis we did has a host of applications for the cryptocurrency industry, for regulators and for legal and law enforcement agencies. We have developed a short briefing paper that summarises the key findings and are actively looking to share the findings across the decentralised finance sphere."
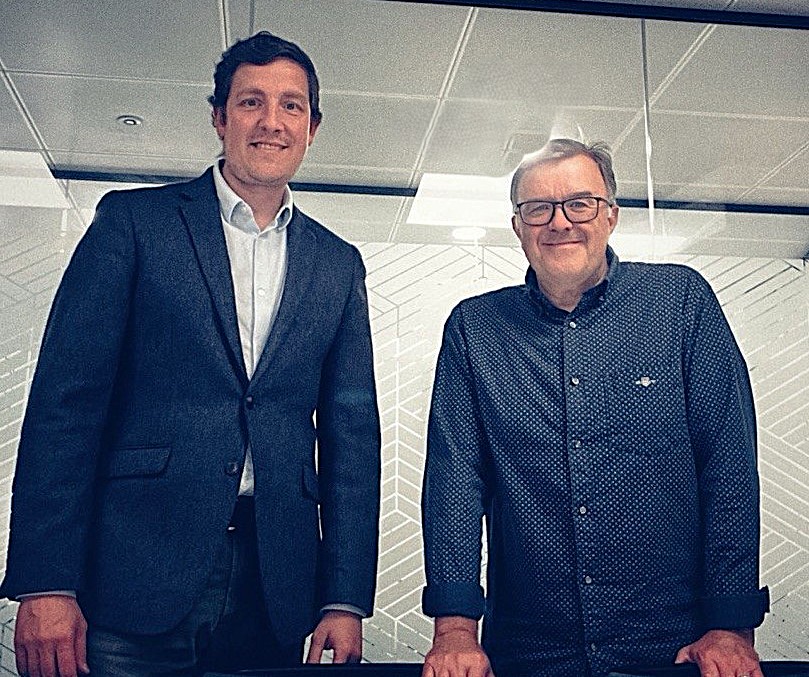 Report authors Remo Stieger (left) a former partner at SyntiFi Risk Intelligence, and Professor Tim Hall of the University of Winchester’s Department of Policing, Criminology and Forensics
This research is the first to combine criminological and On-chain Risk Intelligence (ORI) analysis and to use multiple sources to explore the nature, extent and patterns of attacks on the DeFi ecosystem.
It analysed seven major blockchains where flash loans are available (Ethereum, Base, Optimism, Arbitrum, BNB Chain, Avalanche and Polygon) using SyntiFi’s ORI engine which scanned 20.63 billion blockchain transactions.
Prof Hall was also keen to stress that these were not victimless crimes as the money ultimately belongs to someone.
"As part of our research we spoke to a representative from a platform that had suffered a massive flash loan attack,” he said.
“This cost their investors, in some cases, millions of dollars. The attacker started taunting the platform on social media after the attack and this led to some victims engaging with the attacker and outlining the devastating impacts that the loss of this money had on them."
The key idea is: borrow huge amounts, manipulate/exploit a weaknes, repay the loan and keep the profit, all in one transaction.
Read “Flash in the Pan?: Analyzing Flash Loan Attacks on the DeFi Ecosystem” HERE
Back to media centre